How SOC Managed Services Providers Build Essential Security Readiness for India
Why SOC Managed Services Providers Matter for Indian Healthcare
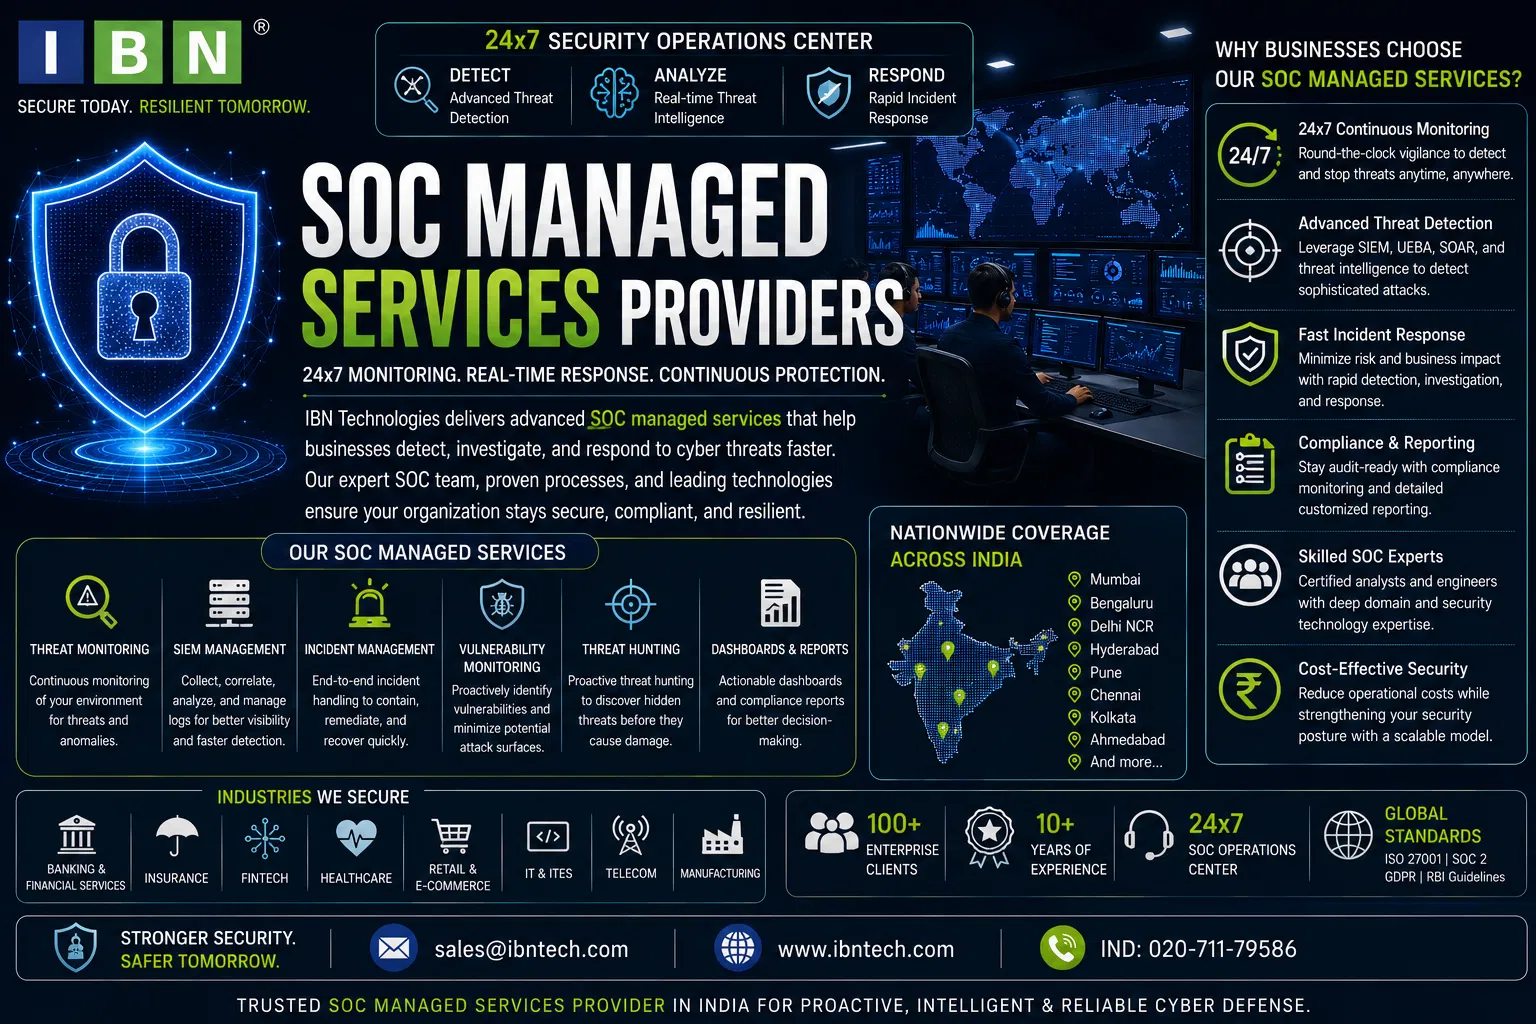
Healthcare organisations increasingly depend on digital applications, connected systems, user accounts, networks, and technology infrastructure to support everyday operations. This creates a security environment where unusual activity can appear across multiple systems and may require timely investigation. soc managed services providers can support healthcare organisations by establishing structured processes for monitoring security events, analysing alerts, investigating suspicious activity, and escalating relevant findings.
The purpose of a managed SOC is not simply to add another security platform. It is to create an operational function around security monitoring so that alerts can be reviewed and handled through defined procedures.
For healthcare teams, this can be particularly relevant when internal IT resources are already responsible for maintaining applications, infrastructure, user access, and other technology operations.
How SIEM Monitored 24x7 by a SOC Supports Healthcare Security
A siem monitored 24x7 by a soc approach combines security-event visibility with ongoing SOC analysis. SIEM technology can collect and organise relevant security events, while SOC analysts can review alerts and investigate activity that requires additional attention.
This distinction matters because collecting security information does not automatically determine whether an event represents a genuine concern.
For example, unusual account activity may require additional context before a security team can decide what action is appropriate. Continuous SOC monitoring can provide an operational process for reviewing such events and escalating relevant findings.
Why Healthcare Security Cannot Depend Only on Automated Alerts
Automated security controls are useful for identifying potential threats, but healthcare organisations also need processes for interpreting those signals.
An alert may be generated because of unusual authentication behaviour, unexpected access activity, or another security condition. The alert itself may not explain why the activity occurred or whether it is authorised.
Human analysis can provide the contextual review needed to determine whether additional investigation is appropriate.
This is where managed SOC operations can complement existing security technology. Instead of leaving internal teams to manually review every notification, the managed function can provide structured alert analysis and escalation.
From Security Event to Actionable Finding
A healthcare SOC process can connect several activities into a defined workflow.
Event collection provides security information from systems within the agreed monitoring scope.
Alert analysis examines notifications and considers their relevance.
Investigation looks more closely at suspicious activity and related events.
Prioritisation helps determine which findings require greater urgency.
Escalation communicates relevant findings to the appropriate internal stakeholders.
Response coordination allows internal teams to determine and execute approved actions.
This workflow helps ensure that monitoring does not stop at detection.
What Healthcare Organisations Should Evaluate in a Managed SOC
Selecting soc managed services providers should begin with understanding the healthcare organisation's technology environment.
Important considerations include:
- Applications and systems that require monitoring
- Security events that need to be collected
- Required monitoring coverage
- Alert analysis procedures
- Investigation expectations
- Escalation thresholds
- Internal response ownership
- Communication requirements
- Security reporting needs
- Data-handling and governance requirements
Healthcare organisations should also establish how the managed SOC will coordinate with internal IT, security, application, and system-owner teams.
Why Clear Responsibilities Matter During Security Incidents
A security investigation can involve several teams. An unusual account event, for instance, may require security analysis followed by input from the system owner or identity-management team.
The SOC can identify and investigate the event, but internal teams may need to validate business context or perform approved technical actions.
Defining these responsibilities before an incident occurs can make coordination more predictable.
The goal is not to transfer all security responsibility externally. Instead, the managed SOC should complement internal capabilities while providing a defined security operations layer.
The Role of Continuous Monitoring in Healthcare
Healthcare technology environments can remain operational beyond traditional office schedules. Applications, infrastructure, and connected systems may continue generating security events when fewer internal personnel are available.
Continuous SOC monitoring can provide an established process for reviewing security activity during those periods.
The phrase siem monitored 24x7 by a soc describes an operating model in which security-event information is continuously monitored while SOC personnel provide analysis and investigation rather than relying solely on automated detection.
This distinction can be important when organisations evaluate whether their existing security monitoring provides sufficient operational coverage.
Benefits of Managed SOC Operations for Healthcare
A managed SOC model can support healthcare organisations in several ways.
- Ongoing security visibility: Relevant events can be monitored through a defined operational process.
- Alert investigation support: Suspicious activity can receive structured analysis.
- Prioritised security attention: Events can be assessed according to their potential relevance.
- Defined escalation: Important findings can be communicated to appropriate internal teams.
- Additional operational capacity: Internal IT personnel can receive support with security monitoring activities.
- Improved coordination: Security findings can move through established communication and response processes.
These benefits depend on the monitoring scope, available security data, internal procedures, and agreed service responsibilities.
Healthcare Scenario: An Unusual User Account Event
Consider a healthcare organisation where employees use digital applications to support administrative and operational activities.
Security monitoring identifies unusual authentication activity involving a user account. The event is reviewed by the SOC rather than immediately treated as a confirmed security incident.
The analyst examines related activity and determines whether the pattern requires further investigation. If the finding is significant, it is escalated according to the agreed procedure.
The internal healthcare IT team can then validate the user's activity and take appropriate action based on organisational policy and available evidence.
This process demonstrates why security readiness depends on having a defined path from detection through investigation and escalation.
Managed SOC Checklist for Healthcare Organisations
Before selecting a managed SOC service, healthcare teams should clarify:
- Critical technology environments within scope
- Security logs and events available for monitoring
- Required monitoring schedule
- Alert-prioritisation requirements
- Investigation procedures
- Escalation contacts
- Internal response responsibilities
- Reporting expectations
- Security governance requirements
- Processes for reviewing service effectiveness
A documented operating model can help reduce ambiguity when suspicious activity requires coordinated attention.
Governance and Data Protection
Security monitoring should operate alongside the organisation's wider information-security and data-protection framework.
Healthcare organisations should maintain appropriate access controls, security policies, incident-management procedures, risk-management practices, and data-protection measures.
Where recognised information-security frameworks such as ISO 27001 apply, SOC monitoring should be considered within the broader control environment.
Organisations should also determine how security-event information is handled and ensure that monitoring practices align with applicable legal, regulatory, contractual, and internal requirements.
Strengthening Security Readiness Through Managed Operations
Security readiness depends on more than having security technologies in place. Healthcare organisations also need processes that connect detection, analysis, investigation, escalation, and response.
soc managed services providers can support this operational model by providing structured security monitoring and investigation capabilities that complement internal teams.
For Indian healthcare organisations, a managed SOC can therefore serve as an additional layer of security operations, helping teams maintain visibility across defined technology environments while establishing clearer procedures for handling potentially significant security events.
Contact Us:
IND- 02067680404
IBN Technologies Ltd.
E-mail: - sales@ibntech.com

 English
 Arabic
 French
 Spanish
 Portuguese
 Deutsch
 Turkish
 Dutch
 Italiano
 Russian
 Romaian
 Portuguese (Brazil)
 Greek
 Cehoslowakia