Managed SOC SIEM: What Is a Reliable Choice for Indian Banks
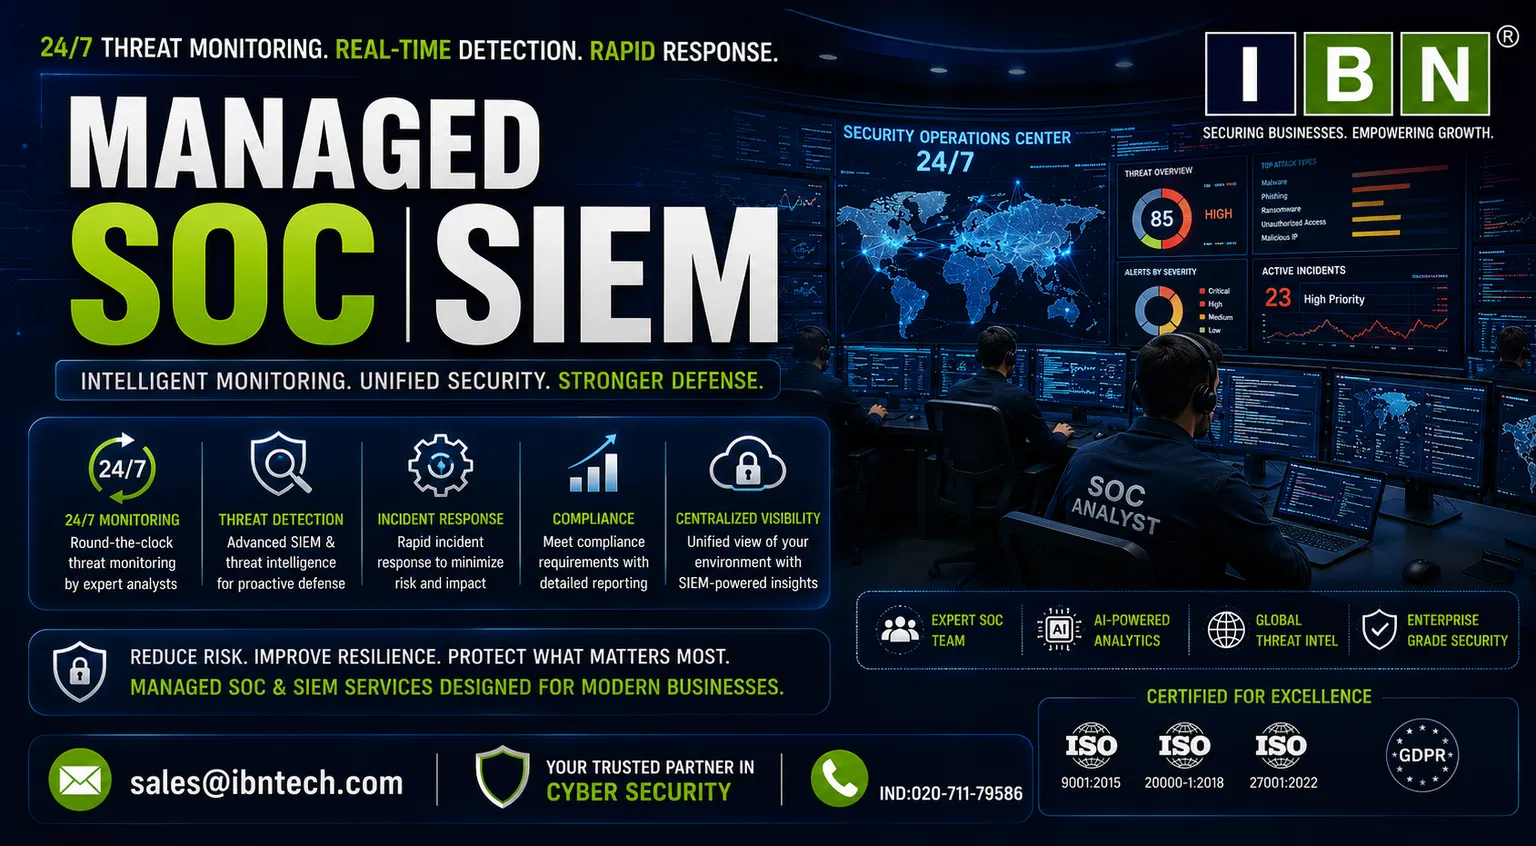
Understanding Managed SOC SIEM Costs for Indian BFSI
For Indian BFSI organizations, managed SOC SIEM brings security monitoring, event correlation, alert investigation, and incident response into a structured service model. It can help banks, insurers, fintech businesses, and financial service teams manage security visibility across applications, endpoints, networks, identities, and cloud environments.
What determines the cost of managed security operations
There is no single price that applies to every BFSI organization. The cost depends on the size and complexity of the environment, the number of security data sources, monitoring requirements, response expectations, and the level of service required.
Environment scale: More endpoints, applications, network devices, cloud workloads, and users generally create more security events that need to be collected and analyzed.
Monitoring scope: A service covering critical banking applications and privileged identities may require a different operating model from one covering only selected infrastructure.
Response requirements: Monitoring and alert notification are different from investigation, escalation, containment support, and incident response.
Integration effort: Existing firewalls, endpoint security platforms, identity systems, cloud services, and applications may need to feed relevant events into the SIEM.
Why BFSI organizations need a clear cost model
Financial organizations cannot evaluate security operations solely by looking at a monthly service fee. They need to understand what that fee represents and which operational responsibilities remain with internal teams.
A useful commercial assessment starts by separating technology, monitoring, people, response, onboarding, and reporting requirements.
For an organization researching SOC managed service cost for Indian BFSI companies, the most useful question is what security outcomes and operational responsibilities are included in the proposed service.
Service scope: Identify the systems, users, locations, applications, and security technologies included.
Alert handling: Determine whether alerts are simply forwarded or actively investigated by security personnel.
Incident escalation: Establish how serious incidents are communicated and which team owns subsequent action.
Reporting: Clarify what operational and management reporting will be available.
Why conventional security monitoring can become expensive
BFSI organizations often operate multiple security controls. Firewalls, endpoint platforms, identity tools, cloud services, application systems, and network infrastructure can all produce security events.
When these systems are monitored separately, analysts may spend substantial time switching between consoles and manually connecting related activity.
Fragmented investigation: An authentication event may sit in one system while endpoint activity appears elsewhere.
Alert overload: Security teams may receive numerous notifications without enough context to determine which events deserve immediate attention.
Specialist dependency: Complex investigations require people who understand security analytics, identity behavior, network activity, and incident response.
Coverage gaps: Internal teams may struggle to maintain consistent monitoring when security staff are occupied with projects, operational work, or incidents.
Managed SOC SIEM can bring these activities into a more coordinated security workflow.
What should be included when comparing prices
A lower quoted price does not necessarily represent a lower total operating cost. BFSI decision-makers should compare service components on the same basis.
|
Cost consideration |
Questions for the buyer |
|
SIEM |
What data sources and log volumes are included? |
|
Monitoring |
What hours and environments are covered? |
|
Analysts |
Who reviews and investigates security alerts? |
|
Response |
What actions are included after an incident is identified? |
|
Onboarding |
What integration and configuration work is required? |
|
Reporting |
What security and management reports are provided? |
|
Scaling |
How does pricing change when systems or users increase? |
How managed SOC SIEM fits BFSI workflows
Consider a financial organization with customer-facing applications, employee endpoints, privileged administrators, and cloud services. A suspicious authentication event could become more significant when followed by unusual access to sensitive systems.
A centralized SIEM can bring those events together. Security analysts can then investigate the sequence instead of treating every event as an independent notification.
Identity monitoring: Privileged account activity can receive additional attention because compromised credentials may provide access to sensitive systems.
Application visibility: Security events from important applications can contribute to broader incident investigations.
Endpoint analysis: Suspicious processes or malware-related indicators can provide additional context.
Network investigation: Unusual connections can be assessed alongside identity and endpoint activity.
The objective is not to collect every possible log indiscriminately. Relevant data should support useful detection and investigation.
India-specific financial security considerations
BFSI organizations in India need security operations that align with their applicable regulatory, contractual, risk, and data governance obligations. Requirements vary according to the type of institution and services provided.
Regulatory alignment: The security operating model should account for applicable RBI requirements, CERT-In obligations, and other relevant rules.
Audit readiness: Security monitoring should produce records and reporting that help internal risk, compliance, and audit teams review security operations.
Access control: Only authorized personnel should have access to security data and administrative functions.
Incident processes: Roles for identification, escalation, containment, investigation, communication, and recovery should be documented before a significant incident occurs.
How to evaluate a managed SOC proposal
What affects SOC managed service cost for Indian BFSI companies?
The main factors include monitoring scope, security event volume, SIEM requirements, integration complexity, analyst coverage, incident response responsibilities, reporting needs, and service governance. Buyers should compare these components rather than evaluating the quoted price alone.
A practical assessment should establish:
- Which systems will be monitored.
- Which events will enter the SIEM.
- Who investigates high-priority alerts.
- What escalation timelines apply.
- Which response actions remain with the BFSI organization.
- How service expansion is handled.
Can managed SOC SIEM reduce internal security workload?
It can shift defined monitoring and investigation responsibilities to a managed security operation. Internal security, risk, and technology teams can then focus on governance, business priorities, major incidents, and decisions that require organizational authority.
Should BFSI companies monitor every available log?
Not necessarily. Log selection should be based on security value, detection requirements, investigation needs, compliance considerations, retention requirements, and the organization's technology architecture.
FAQs
Is managed SOC SIEM priced only by the number of users?
No. Pricing can depend on multiple factors, including monitored systems, event volumes, service scope, integrations, analyst coverage, and response requirements.
Can a managed SOC work alongside an existing BFSI security team?
Yes. Responsibilities can be divided so that the managed service handles agreed monitoring and investigation activities while the internal team retains governance, risk decisions, and major incident authority.
What should BFSI leaders clarify before approving a SOC service?
They should clarify scope, responsibilities, integrations, escalation procedures, reporting, data handling, service expectations, and how the service will scale as the environment changes.
IBN Technologies provides managed SOC and SIEM services that can support organizations with security monitoring, investigation, incident response, and operational visibility.
Contact Us
IBN Technologies
Phone: +91 20 6768 0404
Email: sales@ibntech.com
 English
 Arabic
 French
 Spanish
 Portuguese
 Deutsch
 Turkish
 Dutch
 Italiano
 Russian
 Romaian
 Portuguese (Brazil)
 Greek
 Hrvatski
 Cehoslowakia